Sample report
See exactly what you'll get.
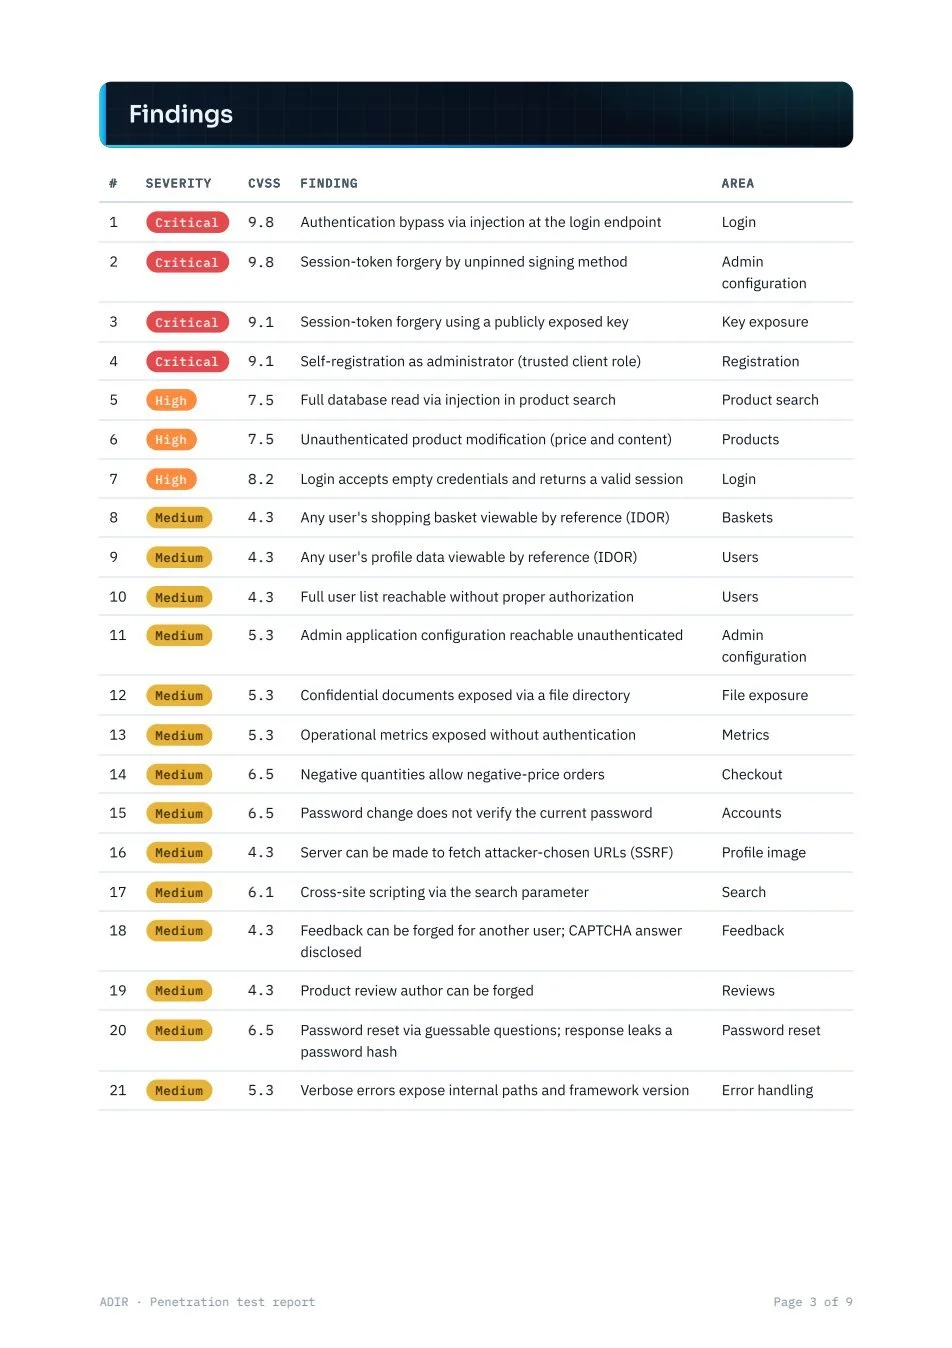
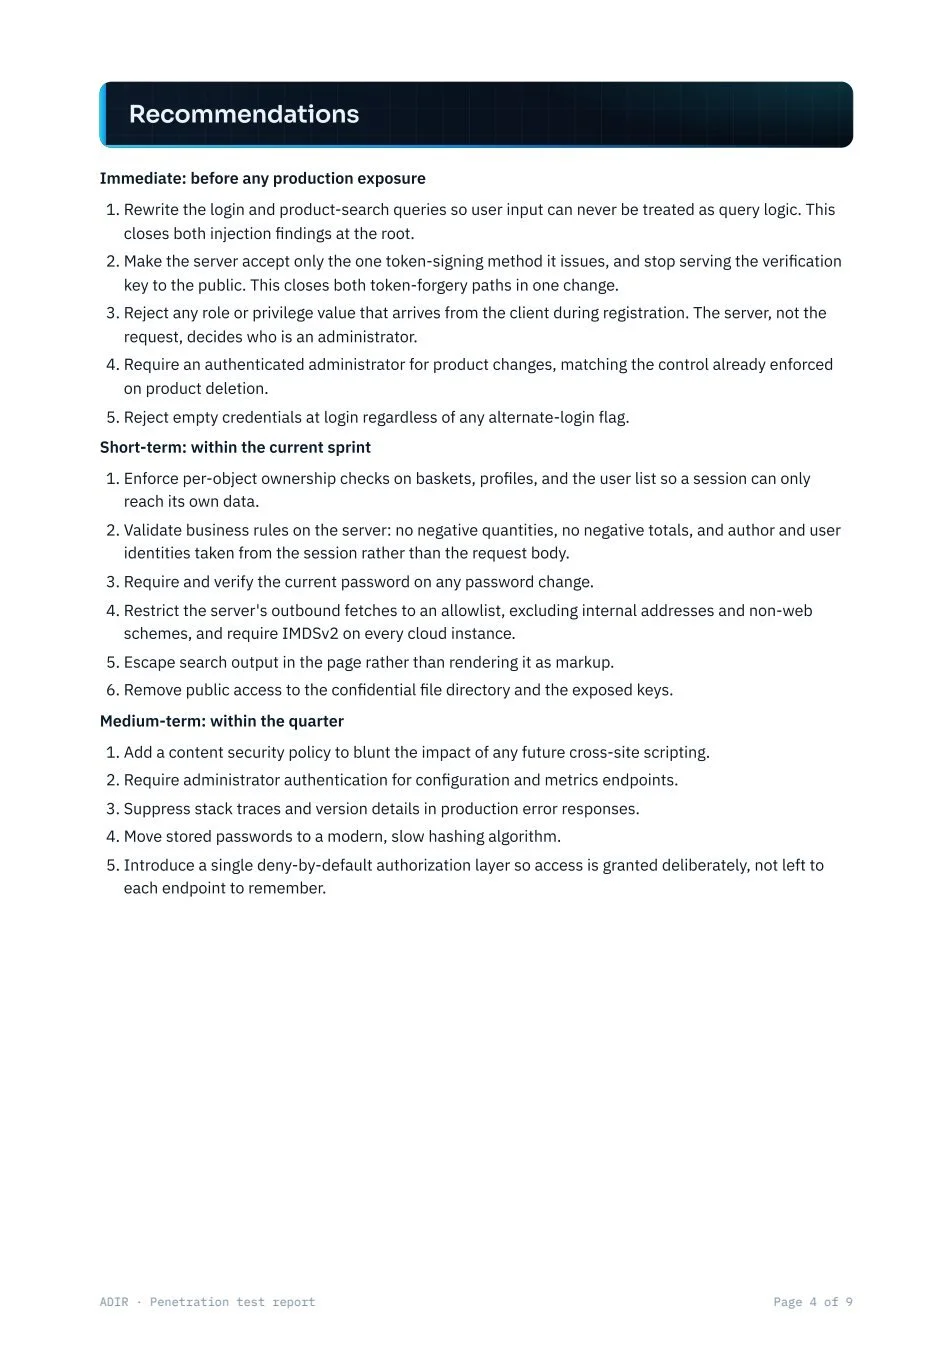
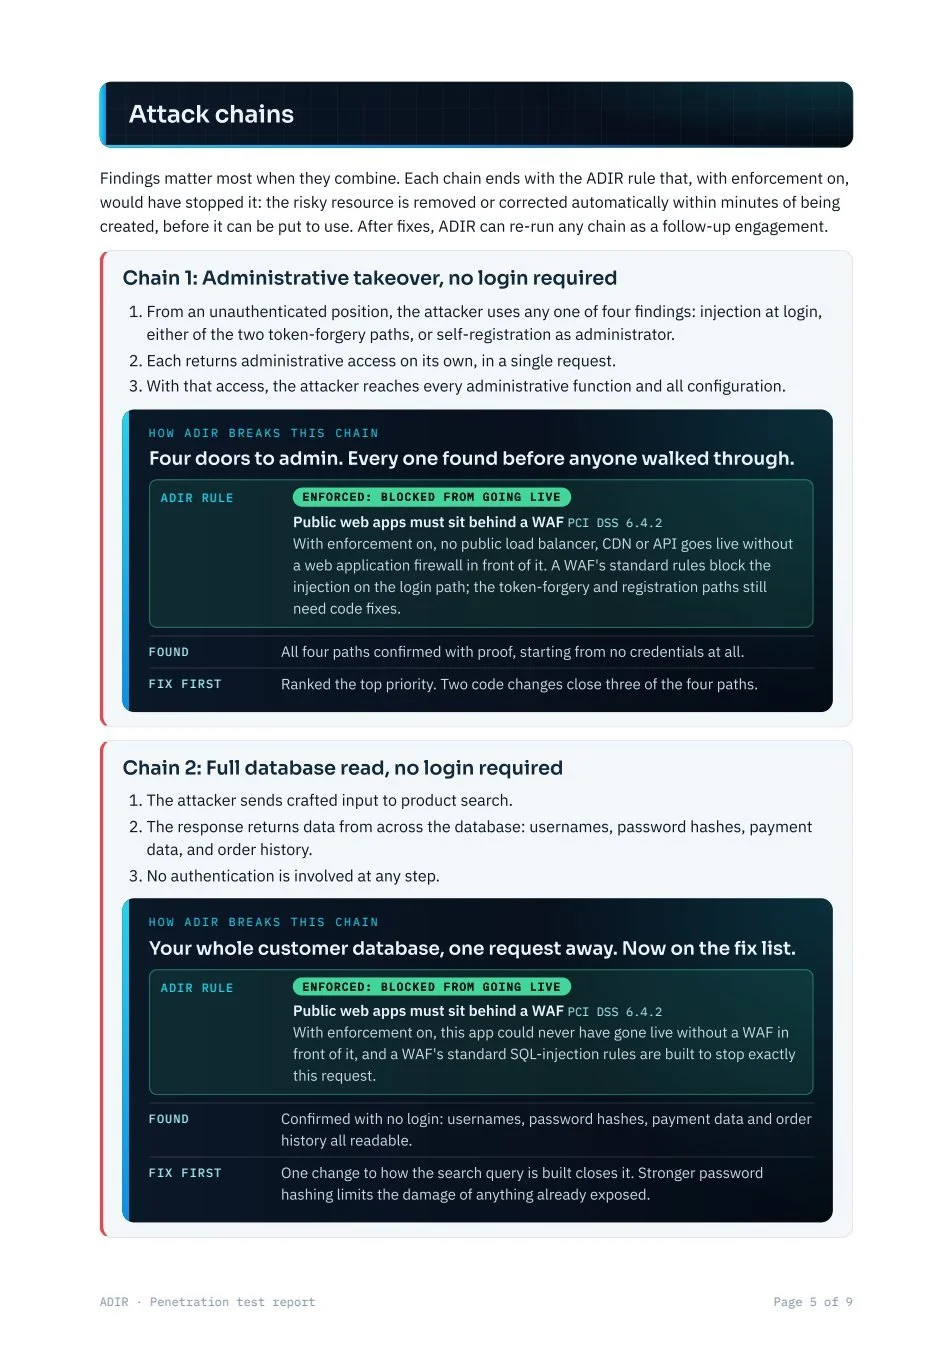
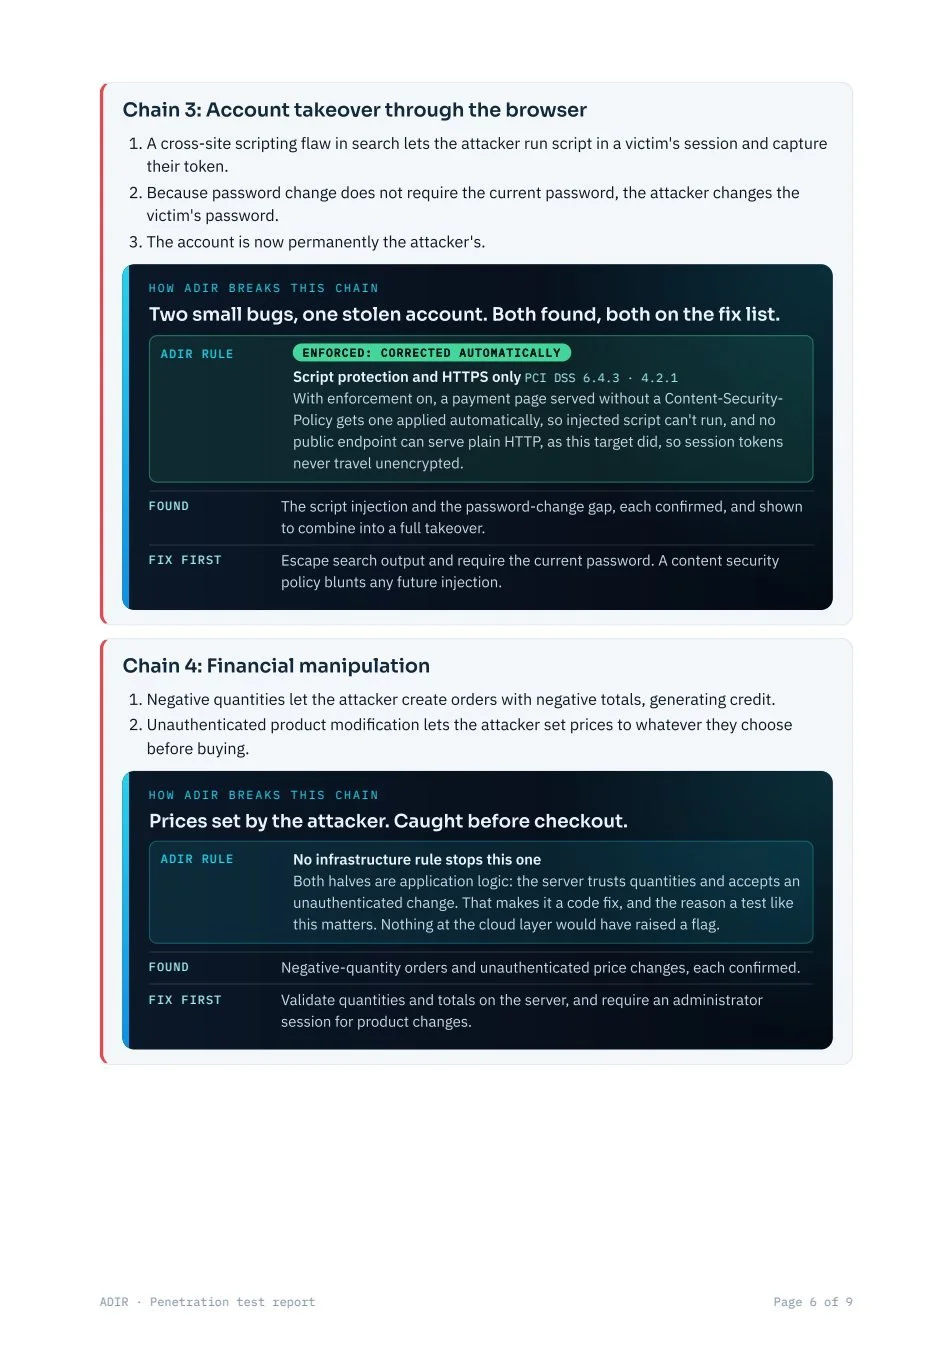
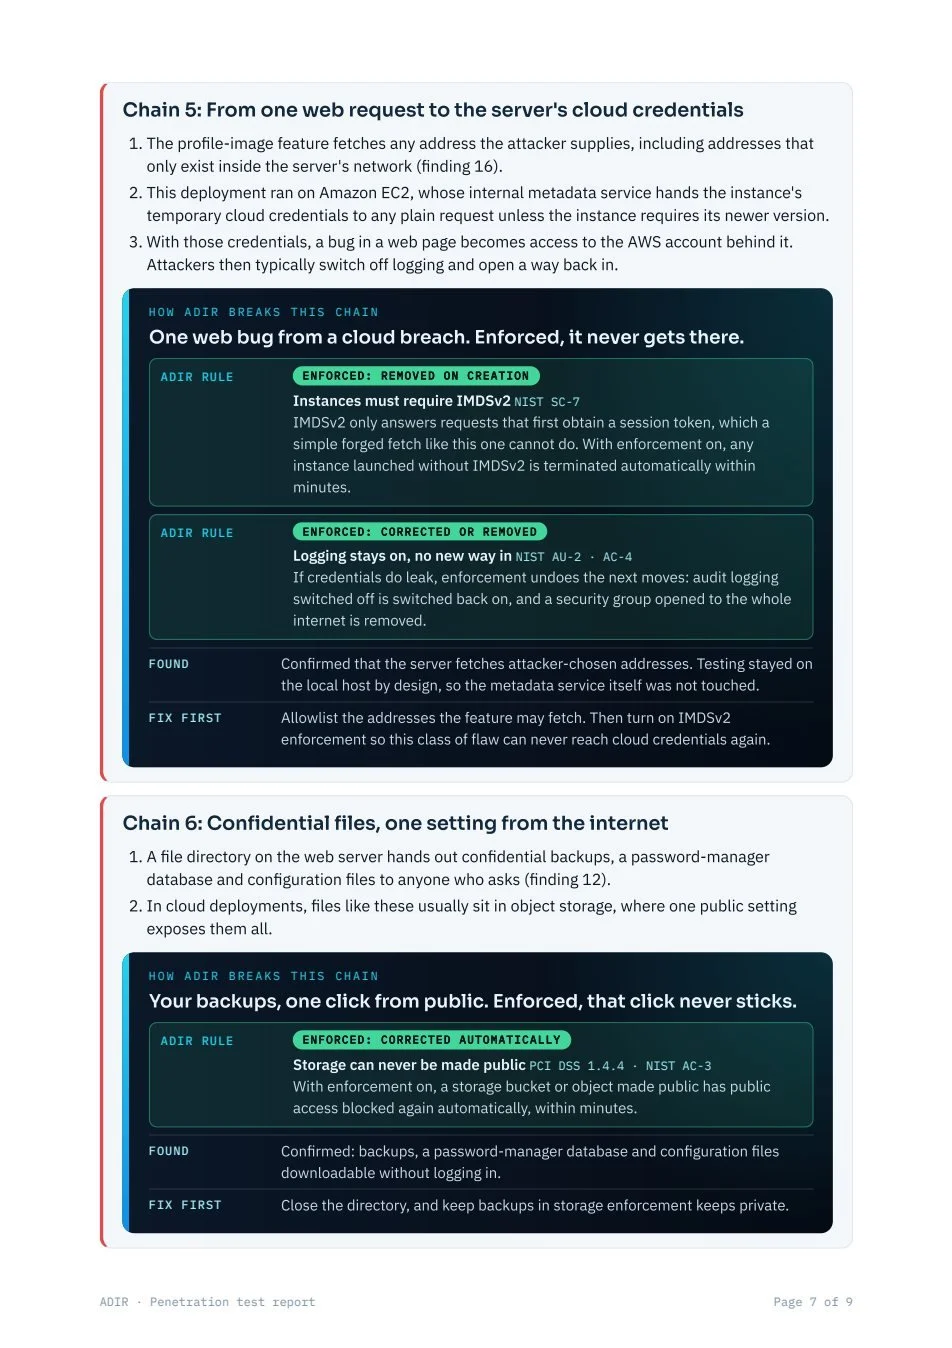
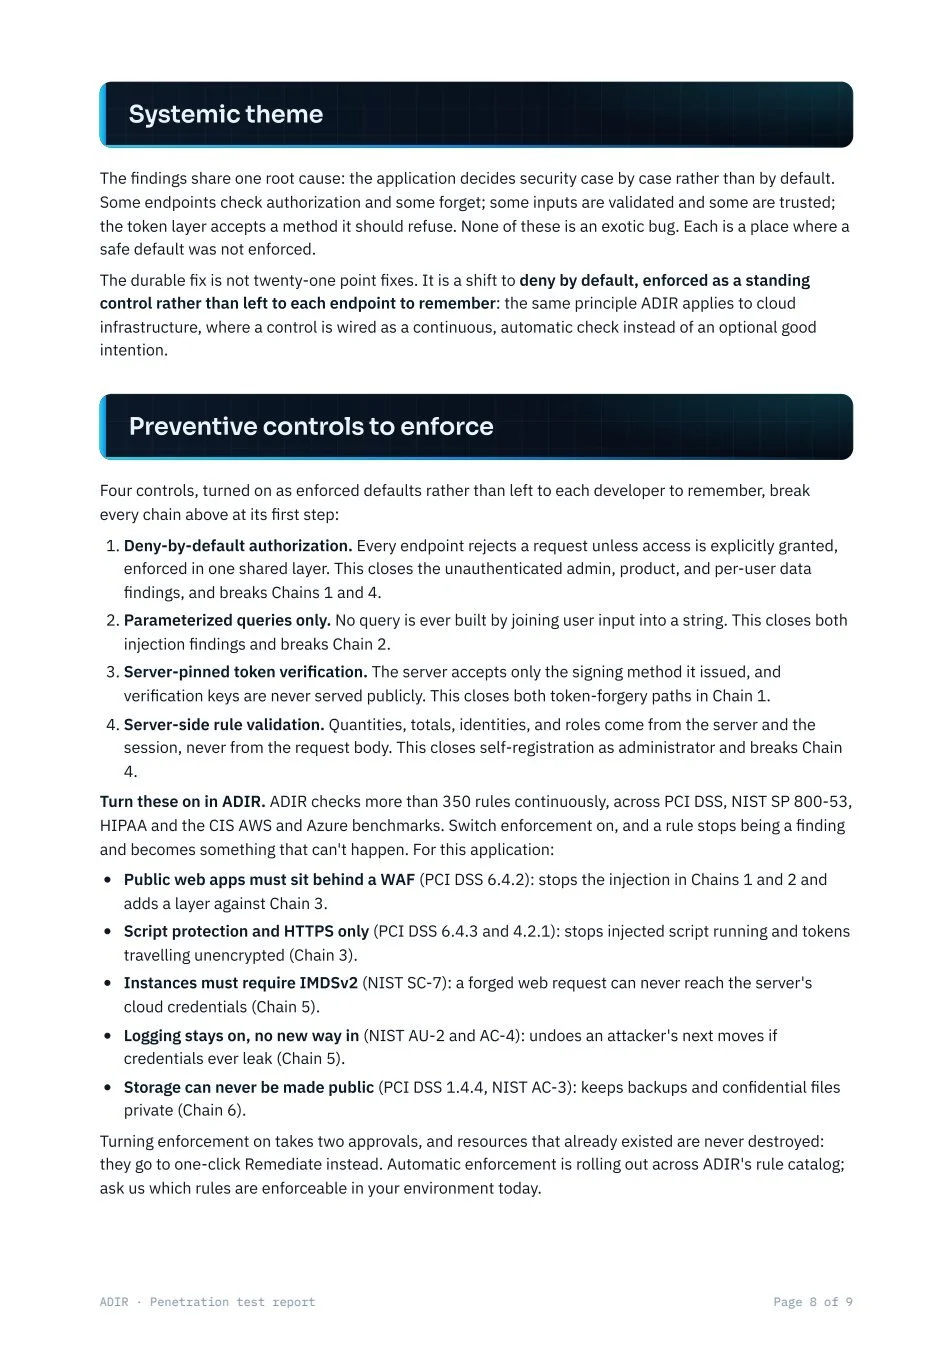
A real report from our standard external penetration test, run against OWASP Juice Shop, an application built to be insecure for security training. Read it right here: 21 confirmed findings, the attack chains they form, and the ADIR rule that stops each chain.
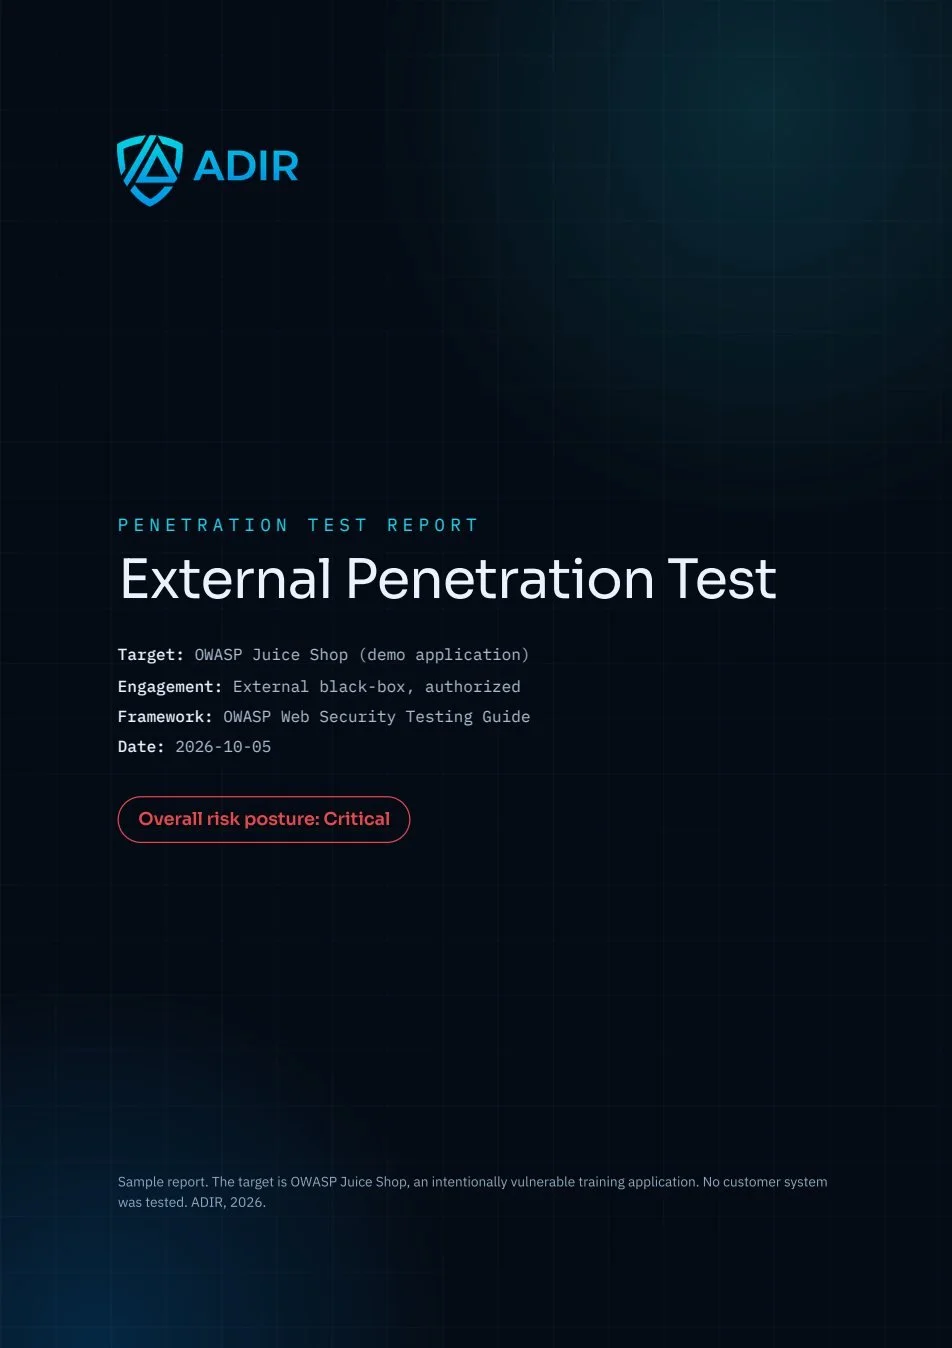
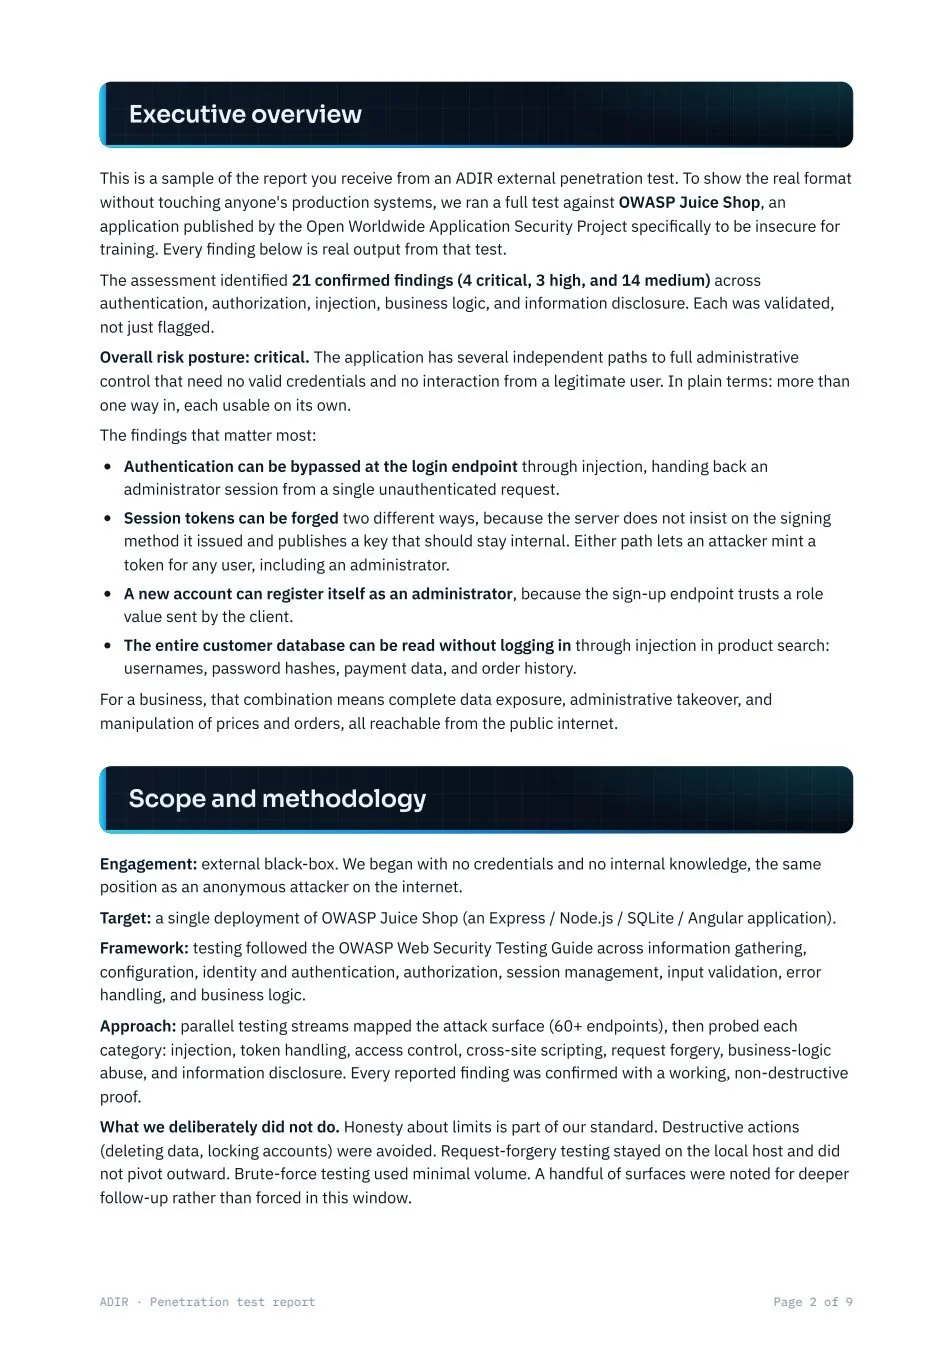
Prefer a copy? Download the PDF
Your report goes further. It adds a confidential appendix with the evidence, proof of concept and reproduction steps for every finding. We leave that out of this public sample on purpose: a document anyone can open shouldn't carry working exploit code.
The target is OWASP Juice Shop, an intentionally insecure application published for security training. No customer system was tested for this sample.